Provisioning → Group Attributes
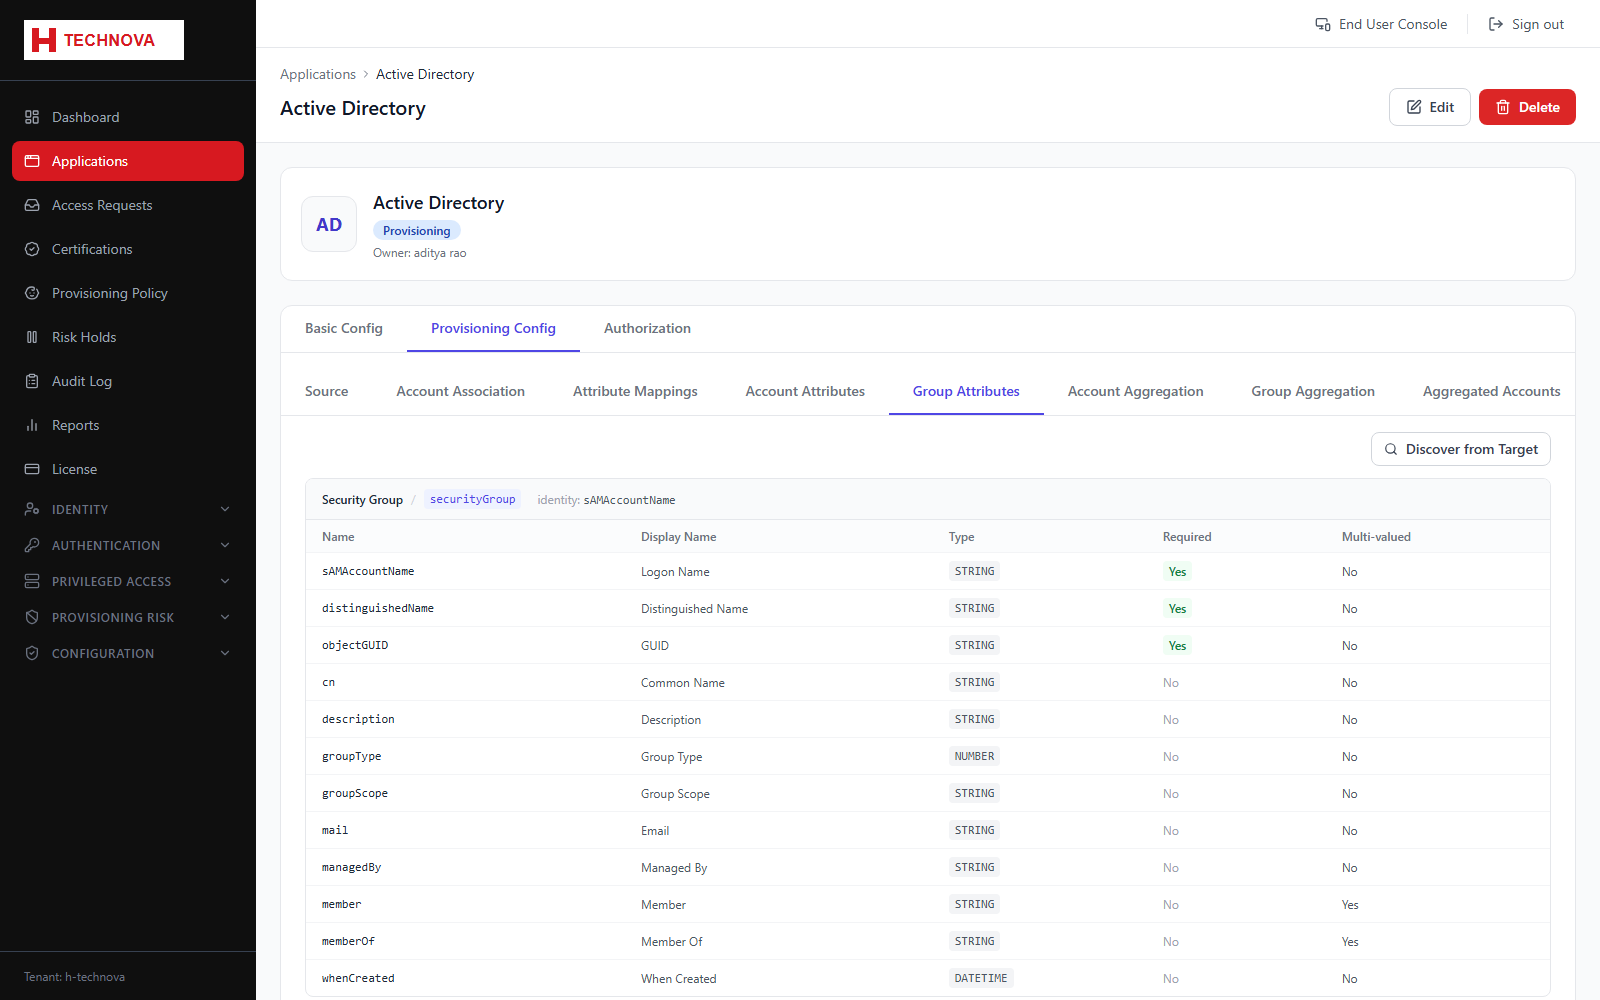
The equivalent schema declaration for groups and entitlements in the target system, used when aggregating groups and when provisioning membership.
How to use it
- Open Provisioning Config → Group Attributes.
- Review the discovered group attributes.
- Add custom attributes as required and set the group identity attribute.
- Save.
Field reference
| Field | Description |
|---|---|
| Group identity attribute | Unique key for a group, commonly its distinguished name. |
| Member attribute | The attribute holding group membership, such as member. |
| Object type | For targets with more than one kind of group-like object (e.g. AWS's IAM Group, IAM Role, and Managed Policy), declare each as its own type here with its own identity attribute and attribute set. |